Tag Archives: News

Apple can’t count….

My opinion of Apple and its practices has never been high. But this is just stupid.

Type in “1+2+3=” in an iOS 11 device’s calculator app, and you get 6 (correctly), but type it in quickly (as demonstrated in this video) and you get 24.

Sure, it’ll no doubt get patched soon and Apple will twist the incident to prove how fast they can push out updates compared to Android. But the point remains – how did such a bug make it past testing? And what OTHER, similarly stupid bugs that have yet to be detected, also make it past testing. And what if one of those bugs was in something fundamental? Something that breaks the functionality of the device? Something like the 1/1/1970 bug that would brick the device, or even the infamous “effective power” bug that would annoying reboot someone’s phone. Or even the famous crashsafari site that was only meant to crash safari but managed to crash the device too (originally, anyway).

OR, was there even ANY testing?

Why everyone is so convinced Facebook is spying on their conversations

Bipul Lama believes Facebook is spying on him.

And he’s got proof, sort of. Lama performed a test. For two days, all he talked about was Kit-Kats.

“The next day, all I saw on my Instagram and Facebook were Kit-Kat ads,” Lama said.

After his Kit-Kat experiment, he successfully repeated it with chatter about Lysol. The 23-year-old musician is now more convinced than ever that Facebook is listening to his conversations through his phone’s microphone.

“It listens to key words. If you say a word enough times, the algorithm catches those words and it sets off targeted ads,” Lama theorized.

Lama is far from alone. The belief that Facebook is actively listening to people through their phones has become a full-on phenomenon. Facebook has, of course, denied it does this. That has done little to dampen the ongoing paranoia around the theory.

Because it is just a theory… right?

Source: Why everyone is so convinced Facebook is spying on their conversations

Petition · Save Your Uber in London #saveyouruber · Change.org

Save Your Uber in London #saveyouruber

I’ve signed the petition.

Source: Petition · Save Your Uber in London #saveyouruber · Change.org

Dharni – Check it out! Phantom Of The Opera Beatbox with Edyta…

Rarely I post stuff from Facebook due to my bad history with them, but this (via Mashable) is pretty damn good

‘Star Trek Discovery’ premiere review: Smart, serious sci-fi on a slow burn

Another female captain to add to the diverse list of captains of Star Trek vessels. And I’m actually happy it’s finally someone from the East. Even more so, someone with a history of action films. Patrick Stewart had a history of films behind him too, but not all were action, and is mostly famous for his  Shakespeare work.

Source: ‘Star Trek Discovery’ premiere review: Smart, serious sci-fi on a slow burn

App That Paid Users to Exercise Owes Nearly $1 Million for Not Paying Users to Exercise

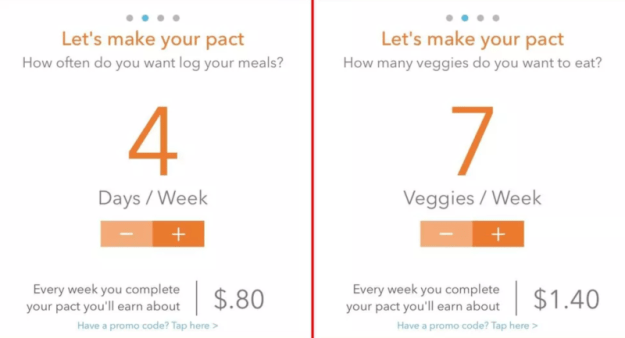
In the capitalistic nightmare we live in, everything has to be a transaction. So, when Pact launched its fitness app that let you make money for working out—or else pay a fee for failing to do so—it seemed to be the perfect motivational tool. There was just one problem: The company apparently wasn’t that great at paying up, and was it too good at collecting fees.

Hah, I remember this app. I actually did try it for a while but failed to see its appeal, or how it could make me continue to exercise. People would only be interested in this if they were really seriously wanting to meet a goal. People demotivated enough, would just cancel the pact/goal and continue on.

Source: App That Paid Users to Exercise Owes Nearly $1 Million for Not Paying Users to Exercise

CCleaner malware outbreak is much worse than it first appeared | Ars Technica

The malware backdoor in this story is quite intriguing. They are targeting specific companies (Samsung, Akamai, Cisco, Microsoft amongst them) and only attempting the second level attack if they are detecting they are being installed there.

The advice mentioned in the article is that anyone who installed the software on their system should REFORMAT THEIR DRIVE. Quite an extreme recommendation. My suggestion – stop using Windows.

Source: CCleaner malware outbreak is much worse than it first appeared | Ars Technica

Google/HTC deal is official, Google to acquire part of HTC’s smartphone team | Ars Technica

So Google has officially hooked up with HTC. How do I feel about this? Rather ambivalent, actually. On one side Google is already using their phones (Pixel), but HTC did roll over to Apple a long time ago without standing up to their bullying tactics – something that made me ditch HTC in favour of Samsung (and, tbh, I’m glad I did). However, this link up means Google gets a dedicated team to work on their phones. Whether this means they’ll become a decent competitor to the other devices, remains to be seen.

Source: Google/HTC deal is official, Google to acquire part of HTC’s smartphone team | Ars Technica

Linus Torvalds Invites Attackers to Join the Ke… » Linux Magazine

Torvalds is not a huge fan of the ‘security community’ as he doesn’t see it as black and white. He maintains that bugs are part of the software development process and they cannot be avoided, no matter how hard you try. “constant absolute security does not exist, even if we do a perfect job,” said Torvalds in a conversation with Jim Zemlin, the executive director of the Linux Foundation.

“As a technical person, I’m always very impressed by some of the people who are attacking our code,” Torvalds said. “I get the feeling that these smart people are doing really bad things that I wish they were on our side because they are so smart and they could help us.”

Source: Linus Torvalds Invites Attackers to Join the Ke… » Linux Magazine

Apache bug leaks contents of server memory for all to see—Patch now | Ars Technica

Another vulnerability hits the news. Whilst similar to heartbleed in leaking memory contents, it does not seem to be too risky if you’re running it as a single user, and the memory leak isn’t huge quantities.

Saying that, this vulnerability also may also affect cloud systems. For example, on AWS, (which has httpd), doing a version check:

$ httpd -v
Server version: Apache/2.4.27 (Amazon)
Server built: Aug 2 2017 18:02:45

However, without knowing how Amazon have setup Apache behind the scenes, are we able to say definitely that we are/aren’t affected?

Source: Apache bug leaks contents of server memory for all to see—Patch now | Ars Technica