Category Archives: Security

Blogger Pulls Off $30,000 Sting to Get Her Stolen Site Back
If you have a domain of your own, especially one for a business, this is a must-read. If you have an easily guessable password, you DEFINITELY must read this.
For several days last week, RamshackleGlam.com –- the domain name that I have owned and operated since March of 2010 –- did not belong to me, but rather to a man who goes by the name “bahbouh” on an auction website called Flippa.com, and who was attempting to sell off the site to the highest bidder (with a “Buy It Now” price of $30,000.00). He promised the winner my traffic, my files, and my data, and suggested that I was available “for hire” to continue writing posts (alternatively, he was willing to provide the winner with “high-quality articles” and “SEO advice” to maintain the site’s traffic post-sale).
I learned that my site was stolen on a Saturday. Three days later I had it back, but only after the involvement of fifty or so employees of six different companies, middle-of-the-night conferences with lawyers, FBI intervention, and what amounted to a sting operation that probably should have starred Sandra Bullock instead of…well…me.
Blogger Pulls Off $30,000 Sting to Get Her Stolen Site Back.
Share this:

Kent Police fined £100,000 after interview tapes abandoned at former station | ICO news release
The ICO’s investigation found that Kent Police had no guidance or procedures in place to makes sure personal information was securely removed from former premises. The problem was made worse due to an apparent breakdown in communications between the various departments involved in the move.<
ICO Head of Enforcement, Stephen Eckersley, said:
“If this information had fallen into the wrong hands the impact on people’s lives would have been enormous and damaging. These tapes and files included extremely sensitive and confidential information relating to individuals, many of whom had been involved in serious and violent crimes. How a police force could leave such information unattended in a basement for several years is difficult to understand.“Ultimately, this breach was a result of a clear lack of oversight, information governance and guidance from Kent Police which led to sensitive information being abandoned. It is only good fortune that the mistake was uncovered when it was and the information hasn’t fallen into the wrong hands.”
Kent Police fined £100,000 after interview tapes abandoned at former station | ICO news release.
Share this:

Port Knocking
Remember when you used to only open the door when a certain pattern of knocks was heard? You can do the same with ports – the so-called “Port Knocking”. It provides another layer of security to your system as ports are not opened until the correct knocking pattern is received.
Haven’t installed or tried this myself, but may do over the weekend.
http://www.boynux.com/how-to-enable-port-knocking-in-linux/?goback=.gde_102999_member_269001685
https://en.wikipedia.org/wiki/Port_knocking
http://www.microhowto.info/howto/implement_port_knocking_using_iptables.html
https://wiki.archlinux.org/index.php/Port_Knocking
http://www.debian-administration.org/articles/268
http://www.zeroflux.org/projects/knock/
Share this:

Fix the iPhone’s Security Bug On Jailbroken Phones without Upgrading

Behind iPhone’s Critical Security Bug, a Single Bad ‘Goto’
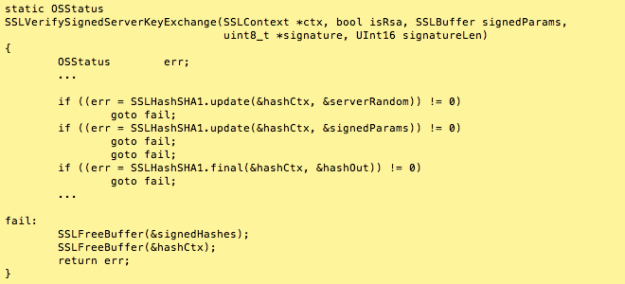
Some software bugs are infinitely subtle and complicated. Others are comprehensible almost at a glance to anyone who dabbled in BASIC as a kid. The iOS 7 bug is in the latter group.
Did you see it? This function is called when a iPhone connects to an encrypted site over SSL: it’s meant to verify that the encryption key is being vouched for — digitally signed — by the operator of the website.
But notice the two “goto fail” lines, one after the other. The first one belongs there. The second is a typo. That extra, duplicative line diverts the program’s execution, like a bypass stent, right past a critical authentication check. The part where the digital signature is actually checked is dead code, never reached.
Behind iPhone’s Critical Security Bug, a Single Bad ‘Goto’ | Threat Level | Wired.com.
Share this:

Something just blew up. In Apple’s face. Big time.
Why Apple’s Recent Security Flaw Is So Scary.
On Friday, Apple quietly released iOS 7.0.6, explaining in a brief release note that it fixed a bug in which “an attacker with a privileged network position may capture or modify data in sessions protected by SSL/TLS.” That’s the understated version. Another way to put it? Update your iPhoneright now.
Oh, and by the way,OS X has the same issues—except there’s no fix out yet.
In simple terms, someone can intercept traffic between you and the site your accessing, and pull of a “Man in the Middle” attack:
I could make all manner of snarky comments on this, but I won’t.
Share this:

Microsoft and Google lead coalition demanding limits on government surveillance
In October, the tech industry’s biggest companies petitioned congress to reform the US Government’s surveillance policies. Now, the firms are taking their pleas global. Microsoft, Apple, Facebook, Google, LinkedIn, Yahoo and AOL (Engadget’s parent company) have banded together to ask the world’s governments to reassess its intelligence practices. This time, however, the firms are presenting more than a strongly worded letter – they’ve laid out five core reform principals, detailed both on an official website and in full-page ads in national publications.
Continue reading


 Blender Fox

You must be logged in to post a comment.